The Problem: The Nightmare of Manual USB Mass Deployments
Imagine your company just received 15 new PCs for the development team. Or perhaps your lab needs 30 workstations re-imaged after a pentesting session. What is the traditional sysadmin approach? Grab two or three Ventoy USB drives, run from desk to desk, plug them in, select partitions, and wait for files to extract.
This approach is exhausting. Deploying 15 machines with two USB drives usually eats up an entire morning—roughly three to four hours straight. That is without considering flaky USB sticks, corrupted flash chips, or accidentally flashing outdated ISOs across departments. If management expects 50 machines ready before lunch, manual methods simply fall apart. A cleaner approach: leverage your existing Gigabit network infrastructure to boot and pull installer images automatically, whether deploying standard installations or modern bootable container operating systems.
Core Concepts: How Do PXE Boot, dnsmasq, and iPXE Work?
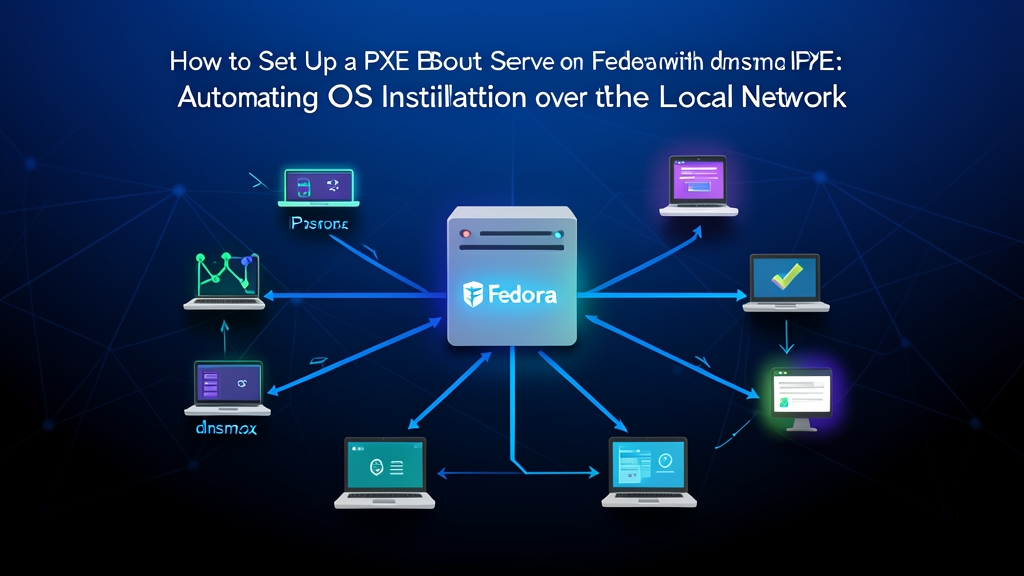
The mechanism is straightforward. When a workstation powers on, its network interface card (NIC) broadcasts a request across the local network asking: “Can anyone provide an IP address and a bootloader?”.
- PXE (Preboot Execution Environment): An industry-standard bootloader environment embedded in NIC ROM and UEFI/BIOS. PXE acquires an IP address from a DHCP server, then downloads the initial bootloader file into RAM to initiate boot.
- dnsmasq: A classic all-in-one Linux tool. Instead of deploying a bulky setup with ISC-DHCP Server and tftpd-hpa, dnsmasq packs DNS, DHCP Proxy, and TFTP into a single lightweight process using under 15MB of RAM.
- iPXE: An open-source firmware replacement for legacy PXE. Standard PXE only transfers files via TFTP over UDP with small block sizes (typically maxing out at 1–2 MB/s). In contrast, iPXE supports pulling kernels and root filesystems over HTTP/HTTPS. Speeds can easily saturate a 1Gbps network link (~110 MB/s), complete with interactive menus and flexible scripting.
Hands-on: Setting Up a PXE Boot Server on Fedora
Fedora makes an excellent lab server platform thanks to its modern kernel and upstream-fresh packages. You can easily repurpose an existing Fedora workstation to act as a network boot server for your entire office.
Step 1: Install dnsmasq and Nginx
First, install dnsmasq alongside Nginx to deliver ISO files over high-speed HTTP:
sudo dnf install -y dnsmasq nginx syslinux-tftpboot ipxe-bootimgsStep 2: Prepare Bootloader Firmware for TFTP
dnsmasq points to a TFTP root directory to serve stage-one boot binaries to clients. Create the directory and copy the appropriate iPXE boot files for both hardware architectures:
sudo mkdir -p /var/lib/tftpboot
sudo cp /usr/share/ipxe/undionly.kpxe /var/lib/tftpboot/      # For older Legacy BIOS machines
sudo cp /usr/share/ipxe/ipxe-x86_64.efi /var/lib/tftpboot/   # For modern 64-bit UEFI machines
Step 3: Configure dnsmasq in ProxyDHCP Mode
Office networks typically already have a router, such as MikroTik or DrayTek, handling DHCP. Spinning up a second DHCP server will cause immediate IP address conflicts. dnsmasq’s ProxyDHCP feature solves this cleanly: the primary router continues assigning IP addresses, while dnsmasq only injects PXE boot options upon detecting DHCP Discover packets from clients.
Create the configuration file at /etc/dnsmasq.d/pxeboot.conf:
sudo nano /etc/dnsmasq.d/pxeboot.confAssuming your Fedora network interface is enp3s0 and its static IP address is 192.168.1.100, enter the following configuration:
# Listen on the local network interface
interface=enp3s0
bind-interfaces

# Run in ProxyDHCP mode on the local subnet (no IP range allocation)
dhcp-range=192.168.1.0,proxy,255.255.255.0

# Enable the built-in TFTP server
enable-tftp
tftp-root=/var/lib/tftpboot

# Detect client architecture: BIOS (0) or UEFI (7, 9)
dhcp-match=set:bios,option:client-arch,0
dhcp-match=set:efi-x86_64,option:client-arch,7
dhcp-match=set:efi-x86_64,option:client-arch,9

# Serve matching iPXE boot files via TFTP
dhcp-boot=tag:bios,undionly.kpxe
dhcp-boot=tag:efi-x86_64,ipxe-x86_64.efi

# Hand off control to the HTTP boot menu once iPXE is loaded
dhcp-userclass=set:ipxe,iPXE
dhcp-boot=tag:ipxe,http://192.168.1.100/boot.ipxe
Step 4: Create a Boot Menu with an iPXE Script
Once iPXE loads into RAM, it fetches boot.ipxe from Nginx to present an interactive menu. Create this file in your web root:
sudo nano /usr/share/nginx/html/boot.ipxeAdd the following sample menu configuration:
#!ipxe

set menu-timeout 15000
set menu-default fedora-live

:start
menu Network Boot System (PXE Lab Fedora)
item --gap --             ---------------- OS INSTALLERS ----------------
item fedora-live          Install Fedora Workstation 39 (Live)
item local                Boot from local hard drive
item shell                Open iPXE Command Shell
choose --timeout ${menu-timeout} --default ${menu-default} target && goto ${target}

:local
echo Booting from local drive...
exit

:shell
shell

:fedora-live
echo Loading Linux Kernel and Initrd via HTTP (1Gbps)...
kernel http://192.168.1.100/os/fedora/vmlinuz ip=dhcp root=live:http://192.168.1.100/os/fedora/squashfs.img ro rd.live.image quiet
initrd http://192.168.1.100/os/fedora/initrd.img
boot
Next, mount the Fedora ISO and copy vmlinuz, initrd.img, and squashfs.img into /usr/share/nginx/html/os/fedora/. Booting over HTTP takes only 15–20 seconds across a standard Gigabit switch.
Step 5: Configure the Firewall and Start Services
Fedora enables strict firewalld rules by default. Open the required ports for DHCP (67/udp), TFTP (69/udp), and HTTP (80/tcp):
sudo firewall-cmd --permanent --add-service={dhcp,dns,tftp,http}
sudo firewall-cmd --reload

sudo systemctl enable --now dnsmasq
sudo systemctl enable --now nginx
Verify service status:
systemctl status dnsmasq nginx --no-pagerNow it is time to test. Connect an Ethernet cable to the client machine, power it on, and press the key to open the Boot Menu (F12 on Dell/Lenovo or F11 on MSI/HP). Select Network Boot / UEFI PXE, and the menu will load in seconds.
Summary
With just dnsmasq and iPXE on Fedora, you have a lightweight yet blazingly fast network boot server. The ProxyDHCP architecture preserves your existing network configuration while making it easy to expand to Windows PE, immutable spins like Fedora Kinoite, or Ubuntu Server images whenever needed.