Why Passwords Are Becoming Obsolete
Whenever I start a new project, I always ask myself: How can I get users into the app as quickly as possible without them having to struggle to remember a complex string of characters? In reality, passwords are a burden. Users tend to set weak passwords or reuse the same one for every account. If your database is leaked, it’s a security disaster. For those looking for even higher security, building 2FA with Node.js can be a powerful secondary defense.
Last year, I worked on a project for a Japanese client. Our team noticed a drop-off rate of up to 40% at the registration step simply because the password requirements were too strict. Immediately after switching to Magic Links, the conversion rate jumped by 30%. This real-world figure shows that convenience always wins.
Comparing Magic Links with Other Methods
Let’s look at current authentication methods to see why Magic Links are worth it:
- Traditional Passwords: Easy to implement but high risk of Brute force attacks. You also spend extra resources building a cumbersome password reset system.
- OAuth 2.0 (Google, Facebook): Very fast, but you are dependent on third parties. If they change their API or users are hesitant to share personal data, you lose customers.
- Passwordless (Magic Link): Users only need to enter their email to receive a login link. This is the perfect intersection of security and user experience (UX).
Pros and Cons to Consider
Pros: Completely eliminates the worry of forgetting passwords. Hackers can’t guess something that… doesn’t exist. The user experience is also much smoother (frictionless UX).
Cons: You are entirely dependent on the speed of the mail server. Additionally, if a user’s email is hacked, their account on your app is equally at risk.
The Essential Toolkit
To build this system, I prefer using the most lightweight and stable libraries available today:
- Node.js & Express: The standard framework for Backend processing. Many developers start here before learning why I switched from Express to Fastify to handle higher traffic.
- JSON Web Token (JWT): Used to create time-bound tokens, ensuring links don’t last forever.
- Nodemailer: The most popular email library in the Node ecosystem.
- MongoDB: Used for simple user information management.
Step-by-Step Implementation
Step 1: Initialize the Environment
Open your terminal and quickly install the necessary packages:
mkdir magic-link-auth
cd magic-link-auth
npm init -y
npm install express nodemailer jsonwebtoken dotenv mongoose
Step 2: Configure Environment Variables
Never hard-code sensitive information. Use a .env file to manage SMTP details and your Secret Key:
[email protected]
EMAIL_PASS=your-app-password
JWT_SECRET=this-should-be-very-long-and-hard-to-guess
PORT=3000
Step 3: Code the Magic Link Logic
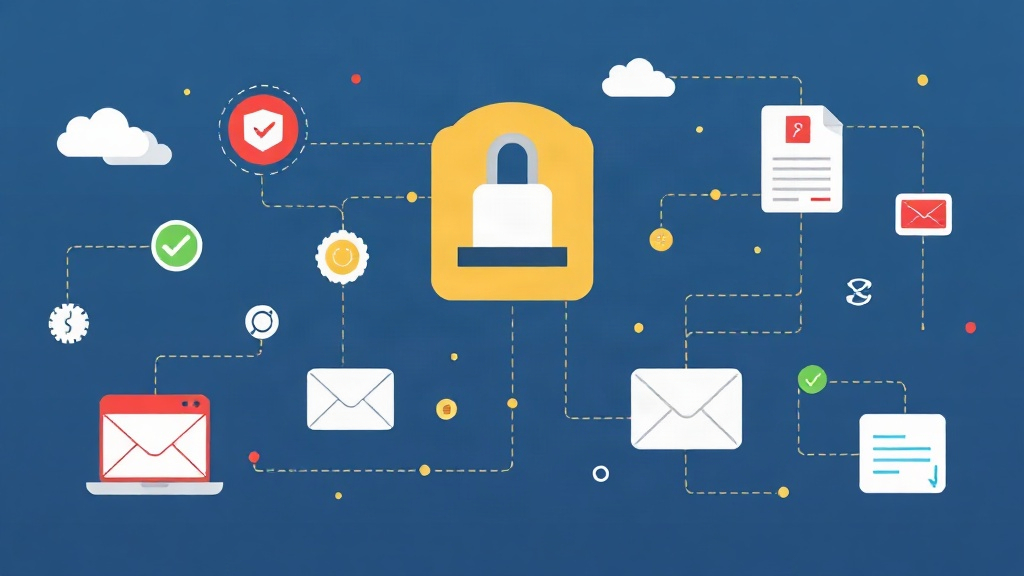
The process is simple: User enters email -> Server generates a JWT token (expires in 15 mins) -> Send a link containing this token via email. Here is the clean email handling code I often use:
const nodemailer = require('nodemailer');
const jwt = require('jsonwebtoken');

const sendMagicLink = async (email, token) => {
  const transporter = nodemailer.createTransport({
    service: 'gmail',
    auth: {
      user: process.env.EMAIL_USER,
      pass: process.env.EMAIL_PASS,
    },
  });

  const magicLink = `http://localhost:3000/auth/verify?token=${token}`;

  await transporter.sendMail({
    from: '"Your App" <[email protected]>',
    to: email,
    subject: 'Your login link',
    html: `<p>Click the button below to enter the system. This link will expire in 15 minutes.</p>
           <a href="${magicLink}" style="padding: 10px 20px; background: blue; color: white;">Login Now</a>`,
  });
};
Step 4: Handle the Login Endpoint
When the user submits their email, the server runs this logic. Using Valibot vs Zod can help ensure the email format is correct before processing.
router.post('/login', async (req, res) => {
  const { email } = req.body;
  // Generate short-lived token
  const token = jwt.sign({ email }, process.env.JWT_SECRET, { expiresIn: '15m' });

  try {
    await sendMagicLink(email, token);
    res.status(200).json({ message: 'Check your inbox!' });
  } catch (error) {
    res.status(500).json({ error: 'Could not send email, please try again later.' });
  }
});
Step 5: Verification on Link Click
This is when we check if the link is valid. This logic is critical and should be verified using tools like API testing and monitoring with Hurl to ensure reliability.
router.get('/verify', (req, res) => {
  const { token } = req.query;
  if (!token) return res.status(401).send('Token is missing.');

  jwt.verify(token, process.env.JWT_SECRET, (err, decoded) => {
    if (err) return res.status(401).send('Link has expired or been modified.');

    const userEmail = decoded.email;
    res.send(`Hello ${userEmail}, you have successfully logged in!`);
  });
});
Crucial Security Lessons
Using just JWT isn’t enough to call it secure. During operation, I’ve drawn 3 important notes:
- One-time Token: Store the token in the database and mark it as “used” immediately after successful verification. Don’t let a link be used for multiple logins.
- Rate Limiting: Don’t let hackers exploit your server to spam emails. Limit it to a maximum of 3-5 emails within 10 minutes per address.
- Device Checking: If the device requesting the login and the device clicking the link are different (different IP or User-Agent), display a confirmation warning to avoid session hijacking.
Optimizing UX So Users Don’t Get Frustrated
Don’t just show a dry line of text after sending the email. Guide the user to check their Spam folder as well. In a previous project, simply adding the sentence: “If you don’t see the email, wait 30 seconds or check your junk mail” reduced complaint tickets by 50%.
If you have a mobile app, look into Deep Linking. When a user clicks the link in the email on their phone, the app will automatically open instead of the web browser. It feels incredibly professional.
Final Thoughts
Implementing Magic Links isn’t difficult at all, but it brings huge value to both devs and users. With Node.js and Nodemailer, you can set this system up in a single afternoon. If you’re working on an MVP, try this method instead of following the traditional password path. To maintain this flow in production, I recommend setting up Cypress E2E testing for your login journey. Happy coding!